whoami --verbose

Security belongs in the architecture, not in the way.

A Security Architect's perspective on designing safer systems without unnecessary friction. Turning complex decisions about identity, applications, infrastructure and risk into security that works in practice.

Security Architecture / Cybersecurity / Portugal
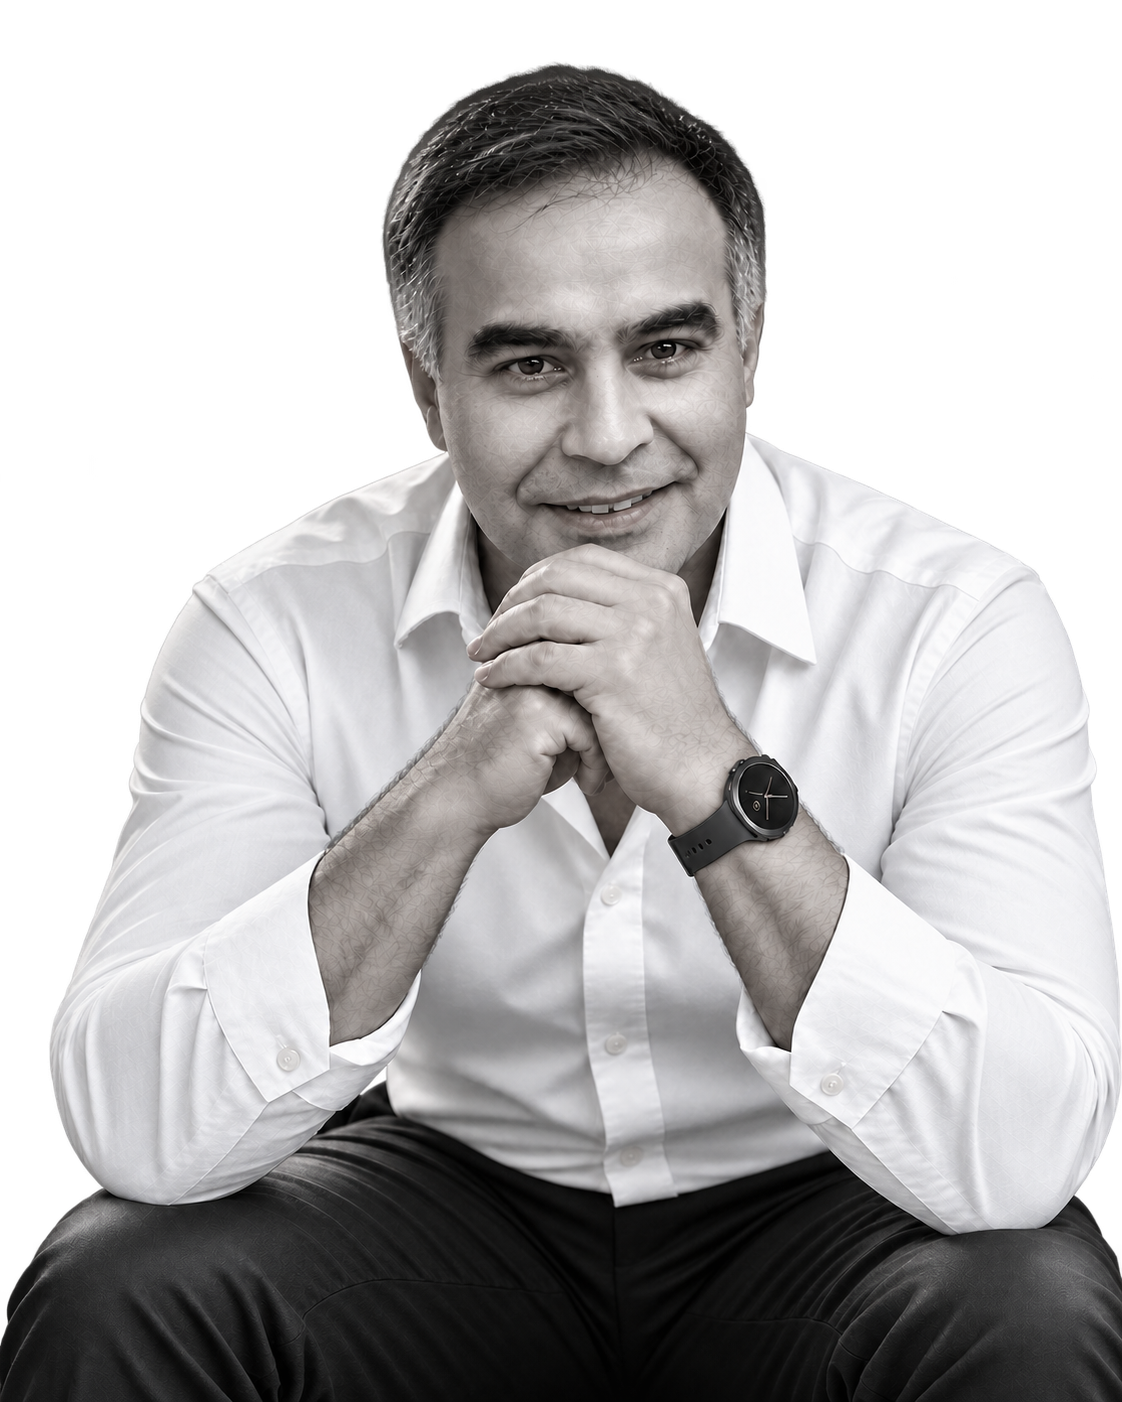
Black-and-white portrait of Pedro Estoura wearing a white shirt, leaning forward with hands clasped
IDEAS · ARCHITECTURE · PRACTICESCROLL TO EXPLORE
SECURE BY DESIGN✳ZERO TRUST✳DEVSECOPS✳IDENTITY & ACCESS✳AI SECURITY
// 01

Real problems. Practical security.

What matters to me is the space between a sound security principle and a system that people can actually operate. These are representative areas of practice; project details are intentionally generalised.

01 / ARCHITECTURE ASSURANCE

Making trust boundaries visible.

Architecture reviews turn diagrams into questions about identity, data flows, exposed interfaces, dependencies and the assumptions that hold a system together.

THE PRACTICE

Threat models, risk decisions and testable security requirements—not just another approval step.

02 / IDENTITY & ACCESS

Knowing who is allowed to do what.

Identity architecture spans authentication, delegated access, privilege and authorisation at the resource. Logging in is only the beginning of a trust decision.

THE PRACTICE

Clearer trust relationships, least-privilege design and lifecycle-aware access.

03 / SECURE DELIVERY

Security that travels with the code.

Application security becomes more sustainable when secure defaults, repeatable checks and evidence are built into engineering workflows.

THE PRACTICE

DevSecOps patterns, verification criteria and a route from findings to fixes.

Individual engagements and institutional systems are not identified here. The focus is on approaches that can be discussed responsibly in public.

// 02

WHO I AM

The person behind the architecture.

I'm Pedro Estoura, a security architect working at the intersection of technology, risk and the people who have to make systems work.

My professional perspective has been shaped by security consulting, technical analysis and the practical constraints of complex organisations. I care about the design decisions that happen before a security finding—and what it takes to turn those decisions into reliable engineering practice.

Today, my areas of focus include security architecture, identity and privileged access, application security, Zero Trust and technical security leadership. They may look like separate disciplines, but the difficult questions almost always cross their boundaries.

I believe good security should simplify the right choices. It should help teams understand risk, build safely and move forward with evidence rather than uncertainty.

Security by design. Clarity by default. Evidence to decide.
MY JOURNEY

Different roles. One direction.

A selective view of the professional themes that have shaped my work. I prefer an honest, evolving record to a list of unverified numbers or titles.

  1. NOW

    Security architecture & technical security

    Connecting architecture reviews, identity, application security and operational risk in the healthcare technology environment.

  2. EARLIER

    Consulting, security analysis & delivery

    Working across disciplines and teams, where security requirements need to survive real platforms, deadlines and operational constraints.

  3. ONGOING

    Learning, research & experimentation

    Exploring emerging standards, automation, AI-assisted engineering and practical ways to verify security as systems evolve.

BEYOND THE ROLE

I like building things to understand them—from small automations and agent workflows to experiments with connected systems. Curiosity is part of how I stay close to the engineering decisions behind the frameworks and standards I write about.

// 03

Where strategy meets engineering.

Bringing architectural thinking, hands-on security and risk together to create solutions that work beyond the slide deck.

01 / ARCHITECTURE

Security Architecture

Secure solution design, architecture reviews, threat modeling and risk-informed decisions with security built in.

Threat ModelingSecure by Design
02 / IDENTITY

Identity & Zero Trust

Identity, privileged access, authentication, authorization and contextual, least-privilege access.

IAM / PAMZTNA
03 / APPLICATIONS

AppSec & DevSecOps

Security throughout the software lifecycle, testable requirements and automated assurance.

OWASPSDLC
04 / PLATFORMS

Cloud & Platforms

Platform hardening, segmentation, secrets management and modern infrastructure security.

CloudKubernetes
05 / ASSURANCE

Risk & Resilience

Governance, standards, audits and business continuity as practical tools for better decisions.

ISO 27001NIST
06 / EMERGING

AI & Automation

Exploring AI agents, automated workflows and AI-assisted engineering with guardrails, observability and accountability.

AI SecurityAutomation
// 03.1

Less noise. Better decisions.

I connect principles to execution — without turning security into an endless series of roadblocks.

01
UNDERSTAND

Start with the right questions.

Understand the goals, data flows, trust boundaries and risks before choosing technologies.

02
DESIGN IN

Turn requirements into practice.

Bring controls into architecture and delivery, with clear ownership and acceptance criteria.

03
VERIFY

Replace assumptions with evidence.

Validate what was built, automate repeatable checks and make residual risks understandable to decision-makers.

CONTEXTTRUSTCONTROLSEVIDENCE
// 04

Read the standard. Question the design.

I follow security standards, emerging protocols and architectural developments to understand what they change in practice—not to collect acronyms. These are independent analyses and research interests, not claims of authorship of the specifications.

01 / APPLICATION ASSURANCEDEEP DIVE · OCT 2026

OWASP ASVS 5.0: beyond the checklist.

The 5.0 release invites a better conversation about application assurance: what needs verifying, at which level, with what evidence—and what architectural decisions follow.

  • What changed in version 5
  • From requirements to evidence
  • Adoption paths and future directions
Read the detailed analysis
02 / IDENTITY PROTOCOLSRESEARCH THEME

OAuth, OpenID Connect & token exchange.

Identity is not authorisation. Delegation, token audiences and RFC 8693 lead to deeper questions about what one system is really trusting another to do.

THE QUESTION Where does delegated trust end?
03 / EUROPEAN DATA ARCHITECTURERESEARCH THEME

EHDS, federation & data protection.

Federated computation, pseudonymisation and secondary use of health data raise architectural questions that go well beyond network connectivity.

THE QUESTION How do you prove appropriate use without exposing more data?
04 / AI-ASSISTED ENGINEERINGRESEARCH THEME

When agents build systems, who verifies the result?

As automation moves from assistance to action, deterministic guardrails, observable behaviour and independent validation become part of the architecture.

THE QUESTION What must remain enforceable outside the model?
// 05

Ideas are better when shared.

Selected technical presentations and structured sessions. Only a public-safe summary is shown when the underlying materials belong to an internal setting.

01 / SELECTED PRESENTATION
INTERNAL TECHNICAL SESSION

Cybersecurity: Principles, Rules & Responsibilities

A technical perspective on secure by design, architecture review, threat modeling, application weaknesses and the responsibility to turn standards into engineering decisions.

SECURE BY DESIGNARCHITECTURE REVIEWTHREAT MODELINGSECURITY REQUIREMENTS

Presentation materials are not distributed publicly. This description reflects general technical themes only.

// 07

EVERY NEXT STEP STARTS WITH A CONVERSATION.

Let's talk about what comes next.

Ideas, architecture, cybersecurity and the questions that don't have simple answers yet.

Professional contact links coming soon